On September 17, 2026, the U.S. Department of the Treasury's Office of Foreign Assets Control (OFAC) designated BitBank, describing it as a key digital asset project controlled by sanctioned Iranian financier Babak Zanjani. Treasury also stated that since June 2026, Hormuz Safe Marine Services Authority had used BitBank to transfer payments it received.
Babak Zanjani is not simply a trading-platform operator. Across several sanctions actions, Treasury has described him as a central financial figure in Iran-related sanctions-evasion networks: using companies, exchange platforms, payment tools, and cross-border commercial arrangements to move funds and provide financial services for sanctioned parties. The digital asset infrastructure around Zanjani has therefore become a recurring focus for sanctions enforcement and on-chain investigations.
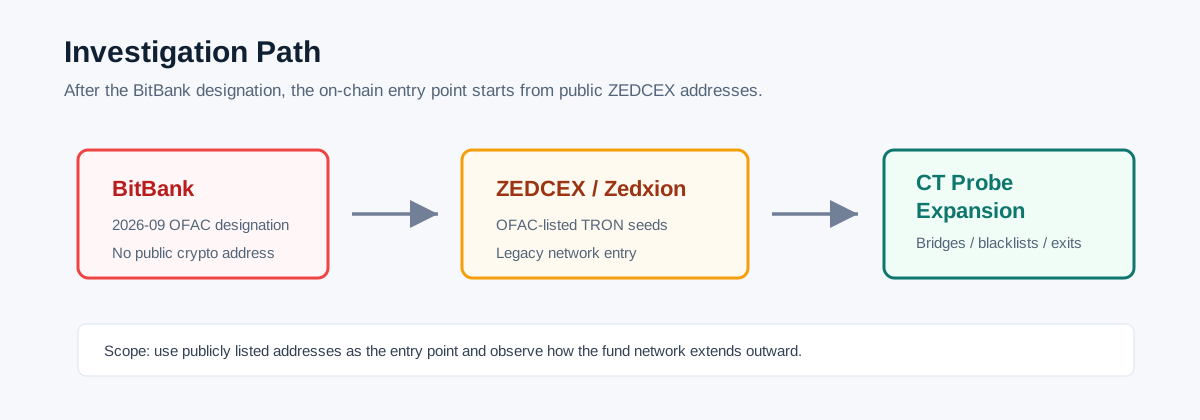
The challenge in this case is clear: BitBank was named, but the public designation did not publish BitBank's on-chain addresses.
ChainTrust therefore used a more verifiable entry point: the publicly listed Zanjani-related legacy digital asset network. Starting from OFAC-listed ZEDCEX / Zedxion TRON addresses, CT Probe examined whether the surrounding network contained expandable high-risk nodes, blacklist exposure, and off-ramp paths.
1. BitBank is the new event, but the on-chain entry point sits in the legacy network
Before BitBank, OFAC had already listed ZEDCEX Exchange Ltd. and Zedxion Exchange Ltd. The ZEDCEX entry directly included seven TRON addresses, which provide a reliable entry point for on-chain investigation.
In other words, this investigation does not begin with a single BitBank wallet. It begins with the Zanjani-related digital asset network that the BitBank designation brought back into focus. The listed ZEDCEX addresses serve as an on-chain doorway into the legacy network's risk extension.
2. CT Probe first confirms: this is not a single-address issue, but a fund network
We used the seven OFAC-listed ZEDCEX TRON addresses as seed addresses. After profiling them, CT Probe found that they show network-like behavior across fund scale, transaction direction, and internal relationships.
Table 1 | Profile of the seven ZEDCEX seed addresses
| ID | Address | Scale | Role |
|---|---|---|---|
| seed1 | TCA9vm...JAv | In 4.03M / Out 2.00M | Fast exit |
| seed2 | TGsNFrg...mEx | In 123.48M / Out 123.32M | Core hub |
| seed3 | TASWbk...Jy8 | In 4.93M / Out 4.93M | Distribution |
| seed4 | TTS9o5...SNa | In 81.99M / Out 82.00M | Clearing |
| seed5 | TCzq6m...YKC | In 0.245M / Out 0.241M | Settlement |
| seed6 | TLvuvpf...roE | In 1.394B / Out 1.406B | Off-ramp |
| seed7 | TNuA5C...MbQ7 | In 25.63M / Out 25.56M | Bridge |
All addresses above are labeled ZEDCEX EXCHANGE LTD / Sanctioned Entity.
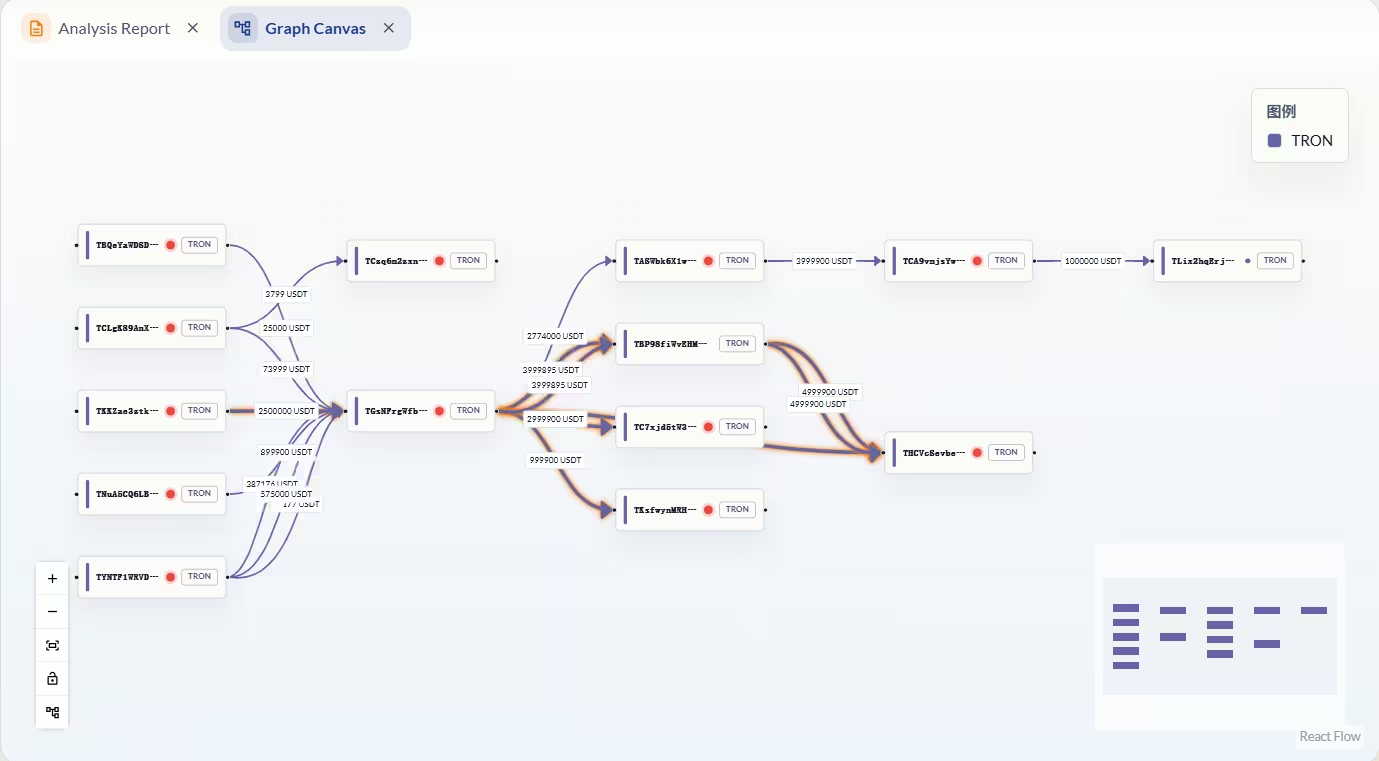
Among them, TGsNFrgWfbGN2gX25Wcf8oTejtxtQkvmEx is a key hub. The report shows approximately 123,479,789 in total inflows and 123,323,611 in total outflows, making its role closer to core aggregation and distribution.
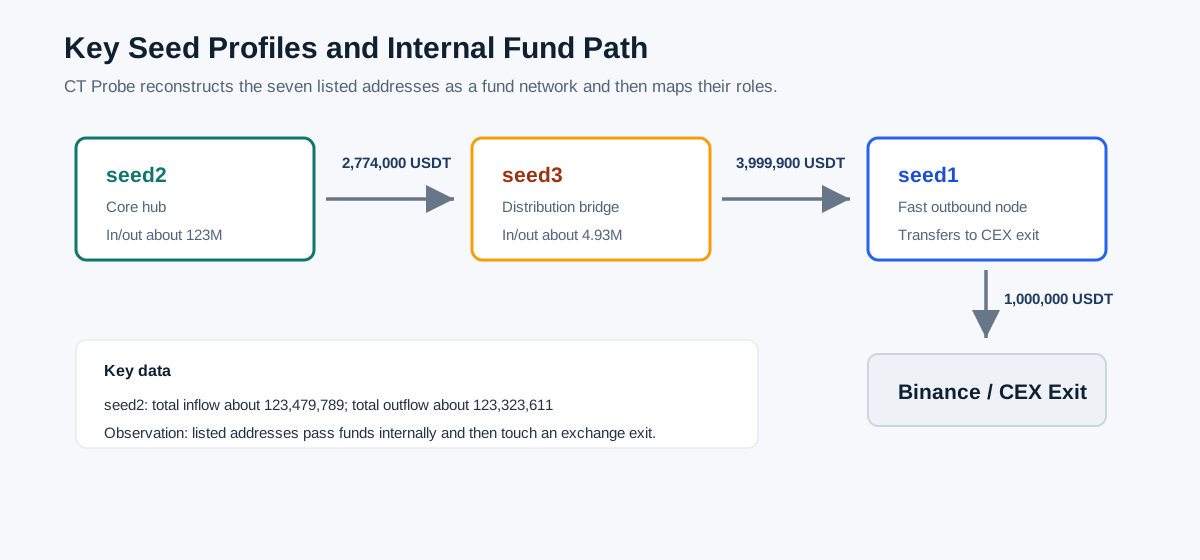
Within the seed set, CT Probe recovered a clear fund path: seed2 transferred 2,774,000 USDT to seed3; seed3 then transferred 3,999,900 USDT to seed1; seed1 then transferred 1,000,000 USDT to a Binance-related CEX off-ramp.
This indicates that the officially listed addresses are not isolated points. They play different roles across aggregation, distribution, and off-ramp paths.
3. The most valuable findings appear outside the seed addresses
If an investigation stops at the OFAC-listed addresses, it can only answer whether those addresses are sanctioned. Compliance investigations usually need the next layer: who those addresses connect to, where funds continue to move, and whether there are intermediary layers or risk exposures not explained in the public notice.
CT Probe identified several categories of risk nodes beyond the seed addresses through one-hop and two-hop expansion.
Table 2 | Key non-seed addresses identified by CT Probe
| Address | Label | Path | Role |
|---|---|---|---|
TKKZae...VCi | banned_unknownentity | seed2 inbound, 38.56M | Upstream risk |
TC7xjd...XV9 | banned_unknownentity | seed2 outbound, 13.96M | Downstream risk |
TYNTF1...giu | usdt_blacklisted | seed2 inbound, 0.96M | Freeze exposure |
TVX78q...b5F | WALLEX | seed5 outbound contact | Sanctioned service |
TCLgK8...BXh | ABCEX | seed5 inbound contact | Sanctioned service |
TBQeYa...NQM | HuionePay | seed5 inbound contact | Special Measures |
TLix2h...naf | Binance CEX | seed1 / seed2 / seed6, ≥ 3.41M | Off-ramp |
TBP98fi...xUE | High-confidence bridge | In / out about 102M | Intermediary |
These are key nodes CT Probe surfaced beyond the seed-address set.
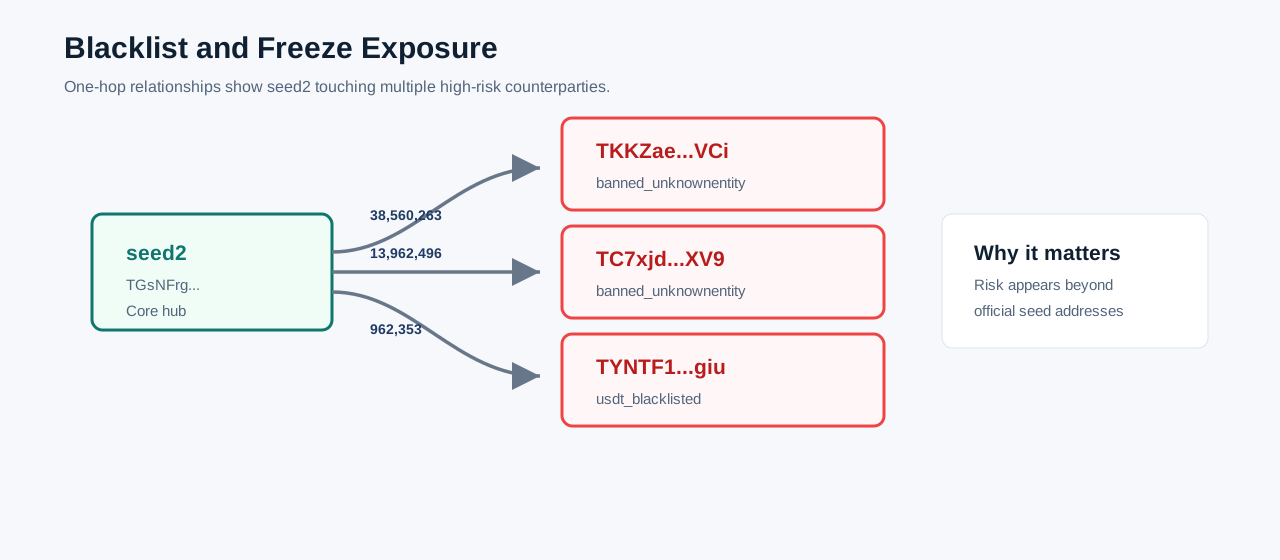
The first category is blacklist or freeze exposure. TKKZae3ztkg1wUK8qLxAN1ReVjQPRjtVCi is labeled banned_unknownentity and appears as a one-hop inbound counterparty to seed2, with approximately 38,560,263.38 in exposure. TC7xjd5tW3D6A9BERmub1SkbhBhw73pXV9 is also labeled banned_unknownentity and appears as a one-hop outbound blacklisted downstream node from seed2, with approximately 13,962,496 in exposure. TYNTF1WRVDTR4iL77m2YDqhHyaTZXBtgiu is labeled usdt_blacklisted and has approximately 962,353 in inbound exposure to seed2.
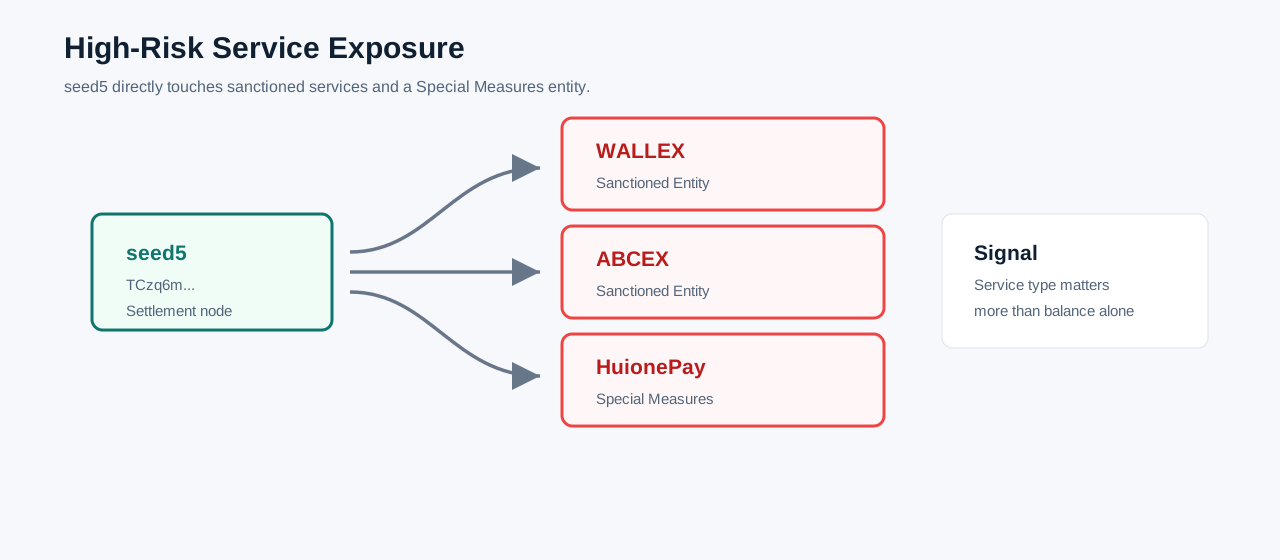
The second category is high-risk service exposure. The report shows that seed5 directly interacted with WALLEX, ABCEX, and HuionePay. WALLEX and ABCEX are labeled Sanctioned Entity, while HuionePay is labeled Special Measures. For compliance teams, this type of information is more important than a balance or transaction count alone because it points to the types of services and risk scenarios that funds may have touched.
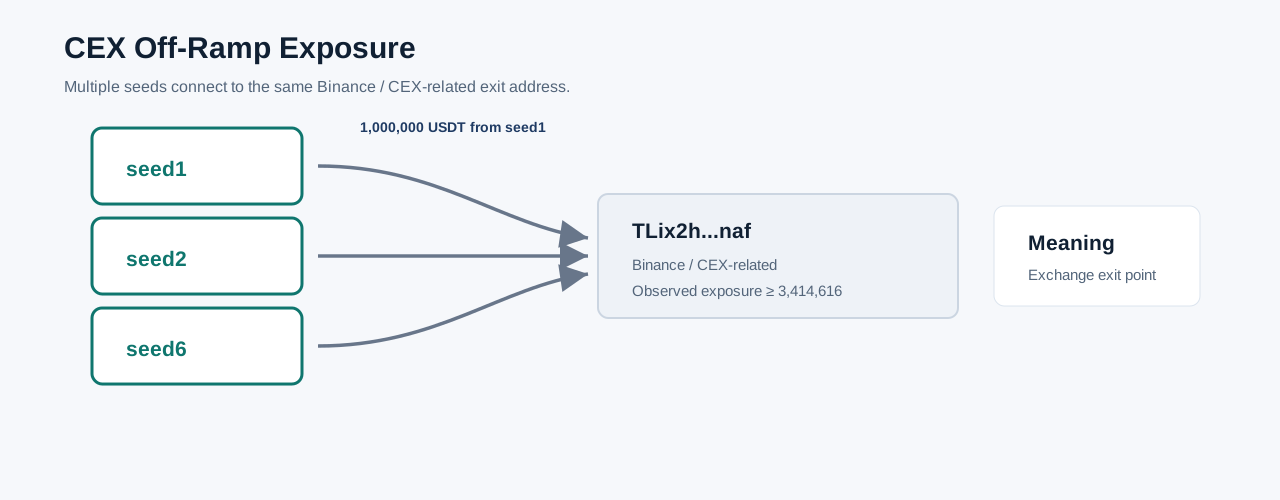
The third category is a CEX off-ramp. TLix2hqErjpzDx3cNYF87XHSAw3Mw7Tnaf is identified as a Binance / CEX-related address. It connects seed1, seed2, and seed6, with no less than 3,414,616 in observed exposure. Its significance is that part of the fund flow reached a centralized-exchange exit.
4. A high-confidence intermediary node worth closer attention
The most useful example for a discovery-oriented investigation in this report is TBP98fiWvEHMvn9BbFAD1V6vqGtQEdHxUE.
CT Probe classified it as a high-confidence extension node because it sits on a structural path connected with seed2 and further links to the blacklisted downstream address THCVcSevbe2XmhfSfeDAHEE7UUoZTQAD9a.
The report shows that TBP98fi... has approximately 102 million in inflow/outflow scale, and the segment toward THCVc... is approximately 16,244,476. Its behavior is closer to a large-value intermediary or aggregation layer.
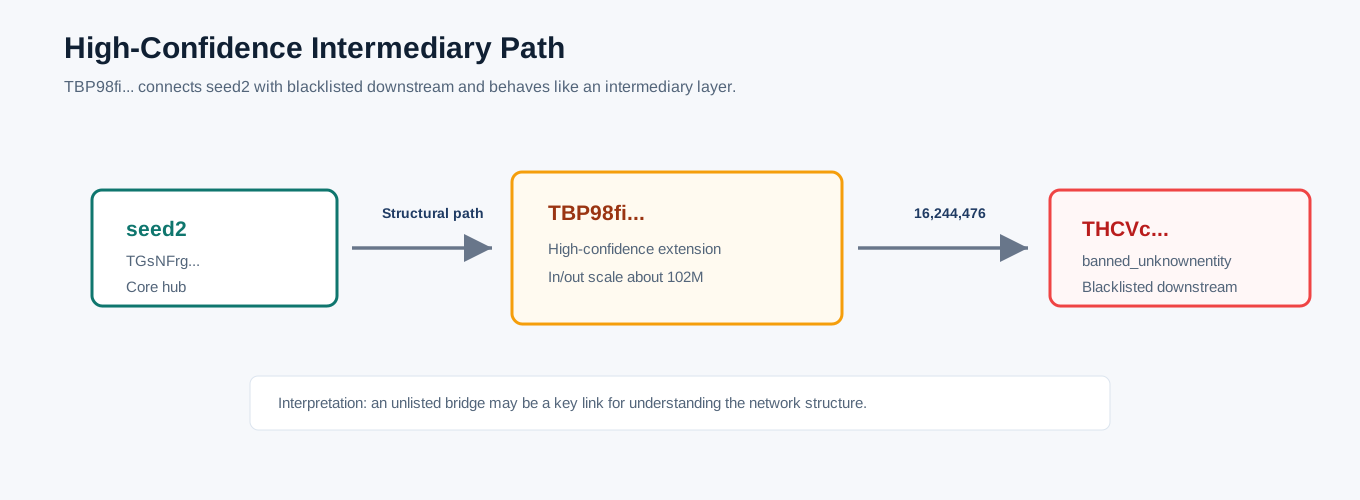
This kind of node is valuable because it may not appear in the public designation, yet it can be a key part of understanding the structure of the fund network. For investigators, the nodes that deserve further review are often those without direct public listing but with clear on-chain roles.
5. What CT Probe adds: from address hits to network discovery
Traditional address screening asks a narrow question: "Does this address hit a list?"
In cases like this, list hits are not enough. Fundraising, payment, clearing, and off-ramping often do not stay within a single address. They are completed through multiple intermediaries, service addresses, and exchange exits.
CT Probe turns a seed address into a readable fund network. It identifies internal relationships among seed addresses, finds shared upstream and downstream nodes, surfaces intermediary bridges, and places blacklisted addresses, sanctioned services, and CEX off-ramps on the same graph. It also helps separate officially listed addresses, high-confidence on-chain extension nodes, and candidate leads that still require review.
In this investigation, using the OFAC-listed ZEDCEX addresses as the entry point, CT Probe identified blacklist exposure, high-risk service exposure, a CEX off-ramp, and a high-confidence intermediary node beyond the seed set.
6. Takeaways for compliance teams
The BitBank case shows that sanctions notices do not always provide complete on-chain addresses. Even when authorities list certain addresses, those addresses are often the entry point rather than the whole risk network.
Compliance teams need to look at the structure behind the addresses: which addresses aggregate funds, which nodes act as intermediaries, which paths connect to blacklisted or sanctioned services, whether funds reach centralized-exchange exits, and which unlisted addresses hold key positions inside the network.
This is where CT Probe is most useful: starting from a known entry point, it opens up the on-chain relationships that sanctions text does not fully describe, and turns the findings into reviewable, explainable, and actionable investigation evidence.
ChainTrust Labs
Learn more about ChainTrust KYT, on-chain risk monitoring, and investigation products:
References
[1] U.S. Department of the Treasury | Operation Economic Outcast Disrupts Digital Asset Exchange Enabling the Iranian Regime | 2026-09-17
[2] U.S. Department of the Treasury | Treasury Further Dismantles Iranian Financier Zanjani's Network | 2026-07-24
[3] U.S. Department of the Treasury, OFAC | Iran-related Designations; Counter Terrorism Designations; Non-Proliferation Designation Update and Designation Removal | 2026-01-30